
UK firms urged to prepare for new cyber security bill
Wed, 28th Oct 2026 (Today)
UK organisations are being urged to prepare for the Cyber Security and Resilience Bill before it becomes law. The legislation would be the biggest change to the country's cyber security rules since the 2018 Network and Information Systems regime.
The measures would bring managed IT service providers and data centres into scope for regulation for the first time, while giving regulators the power to designate critical suppliers. Organisations affected by a reportable cyber incident would have to file an initial report within 24 hours of becoming aware of it, followed by a fuller report within 72 hours.
Penalties would also increase under the proposed framework. For the most serious breaches, organisations could face fines of up to £17 million or 4% of worldwide turnover, whichever is higher. Less serious failures could bring penalties of up to £10 million or 2% of worldwide turnover.
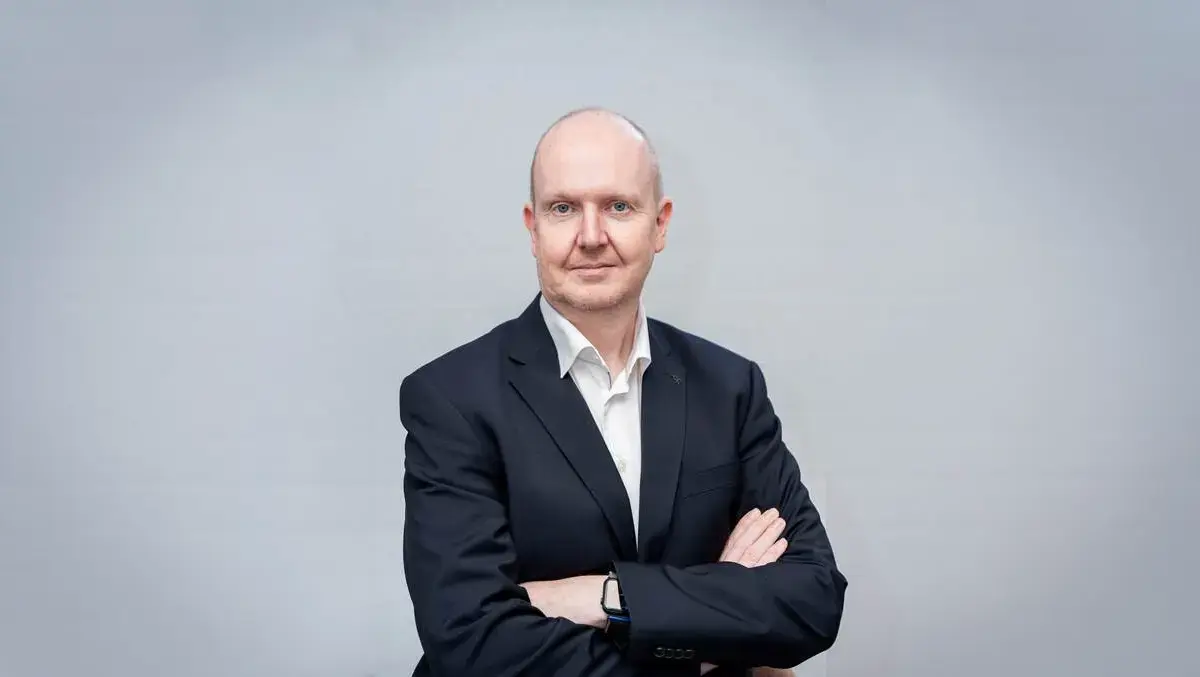
David Robinson, Group Head of Cyber Security at Restore Information Management, said businesses should not wait until the law takes effect before reviewing their exposure. The impact would not be limited to companies directly covered by the rules, he said, because customers in regulated sectors were likely to push tougher standards through their supply chains.
"Cyber resilience cannot be achieved at the last minute. Fixing weak infrastructure, improving supplier oversight and building reliable recovery processes can take years. Any business that starts these processes when the Bill becomes law will already be behind and could end up facing significant fines for that mistake," said David Robinson, Group Head of Cyber Security at Restore Information Management.
Scope check
One of the first questions for businesses is whether they are likely to fall within the scope of the new regime. Medium and large managed service providers would automatically be covered, while regulators including the Information Commissioner's Office and Ofcom could classify other suppliers as critical if disruption to them could seriously affect essential or digital services.
That means smaller companies cannot assume they will be unaffected. If their services support customers operating essential systems, they may face direct oversight or stricter contractual obligations from clients that need to meet the new standards.
"If customers rely on your services to keep essential systems running, you need to prepare for greater scrutiny. Waiting for a regulator to inform you that you're affected will leave too little time to address weaknesses," Robinson said.
Gap analysis
Once organisations understand where they may stand, the next step is to assess whether their current controls would meet the expected requirements. Areas highlighted include data governance, risk management, breach detection, access controls and recovery arrangements.
Businesses can compare their current practices with the proposed requirements, the existing NIS framework and the National Cyber Security Centre's Cyber Assessment Framework, Robinson said. The aim is to identify weaknesses that could disrupt important services or prevent an organisation from detecting, investigating and reporting incidents quickly enough.
"Organisations can compare their current operations against the proposed requirements, existing Network and Information Systems obligations and the National Cyber Security Centre's Cyber Assessment Framework to identify weak spots and the impact they will have on the business," Robinson said.
He added that identifying gaps would not be enough on its own if no team or executive was made responsible for addressing them.
"A gap analysis needs to lead to action. A list of weaknesses with no commitment won't make an organisation more resilient - it's crucial to establish whose responsibility it will be to correct areas of weakness and get things up to scratch," Robinson said.
Reporting duty
The tighter reporting timetable is one of the most immediate operational changes in the Bill. An organisation would need to decide quickly whether an incident is reportable, and the definition would extend beyond incidents that have already caused harm to those capable of adversely affecting services.
That creates a need for round-the-clock decision-making procedures. Businesses are being advised to maintain a 24-hour on-call rota or equivalent arrangement, define escalation criteria and keep regulator and NCSC contact details accessible during an incident.
Supplier links
Another focus is dependency on external providers. Businesses are being encouraged to map where critical information is stored outside the organisation, who can access it, how it moves between systems and how quickly it can be recovered after a breach.
This matters because a company's own response may still fail if a key supplier is slow to identify a breach or pass on evidence needed for reporting and investigation. Clear notification routes and support arrangements with suppliers would help regulated organisations meet their obligations under the proposed law.
"Businesses need to identify where their dependencies on external suppliers are, so that in the event of a breach everyone is on the same page. An organisation may have its own strong internal response plan, but it could still fail in the event of a breach if a critical supplier takes too long to raise the alarm," Robinson said.
Pressure tests
The final recommendation is to test incident plans in realistic conditions rather than rely on written procedures. Suggested exercises include scenarios involving data loss, disruption to physical infrastructure and ransomware, including drills at night or over weekends when staff and suppliers may be harder to reach.
Such tests should check whether teams can contain a threat, retrieve critical information, notify the right bodies and maintain essential services under pressure.
"The middle of a cyber-attack is the worst possible time to discover that backups can't be restored, an emergency contact is out of date, or nobody knows who the breach needs to be reported to. Plans need to be tested under pressure, not just approved," Robinson said.