

Hexnode has expanded its XDR product with new threat detection, alert prioritisation and remediation features, and added support for macOS alongside Windows.
The update broadens the product's reach across endpoint environments and adds external threat intelligence feeds, sandbox analysis and anomaly detection to its detection stack.
Hexnode, the software division of Mitsogo, said the latest version is aimed at security and IT teams looking to reduce the manual work involved in moving from an alert to a response. The product combines endpoint detection with the company's unified endpoint management platform, allowing administrators to investigate incidents and act on affected devices from the same environment.
The expanded system now integrates with Mandiant and Recorded Future to compare endpoint activity with external threat intelligence. It also adds sandbox analysis, allowing suspicious files to be examined in an isolated environment before teams decide how to respond.
Anomaly detection has also been added to flag activity that may not match known threat signatures. Hexnode has also introduced severity-based alert ranking and dynamic device risk scores to help analysts decide which incidents and endpoints need attention first.
Response tools
On the response side, Hexnode has added automated remediation based on pre-set rules and policies. It also offers one-click endpoint isolation, cutting an affected device off from the network while keeping management access available through Hexnode.
The latest release also links incident response more closely with vulnerability management. According to the company, teams can identify vulnerabilities and missing patches through the XDR workflow, then carry out remediation through Hexnode's endpoint management system.
Administrators can set exclusion policies for trusted files, applications and processes to reduce false positives. Custom dashboards let teams tailor what they see based on their roles, while integrations with Splunk and QRadar connect the product to broader security monitoring and reporting workflows.
The update comes as Indian organisations continue to spend more on cyber security tools and operations. Hexnode cited figures showing that 87% of organisations in India expect cyber security budgets to grow, with AI-enabled threat hunting among the leading priorities for AI use in security.
AI link
Hexnode has also linked the product expansion to its broader work on AI features in security operations. Hexnode Genie AI provides plain-language alert summaries and incident explanations drawn from live incident data, along with recommendations on affected systems and possible actions.
Features such as alert prioritisation, asset scoring and automated remediation are designed to support more AI-assisted workflows in security operations centres, according to the company. Those additions suggest Hexnode is positioning the product not only as a detection tool, but also as a system for triage and operational response.
For customers, the main shift is that Hexnode XDR now covers both Windows and macOS endpoints while linking investigation, containment and patching more closely than before. In practice, that means security teams can assess a suspicious event, isolate a device, review vulnerabilities and apply fixes without switching between as many separate tools.
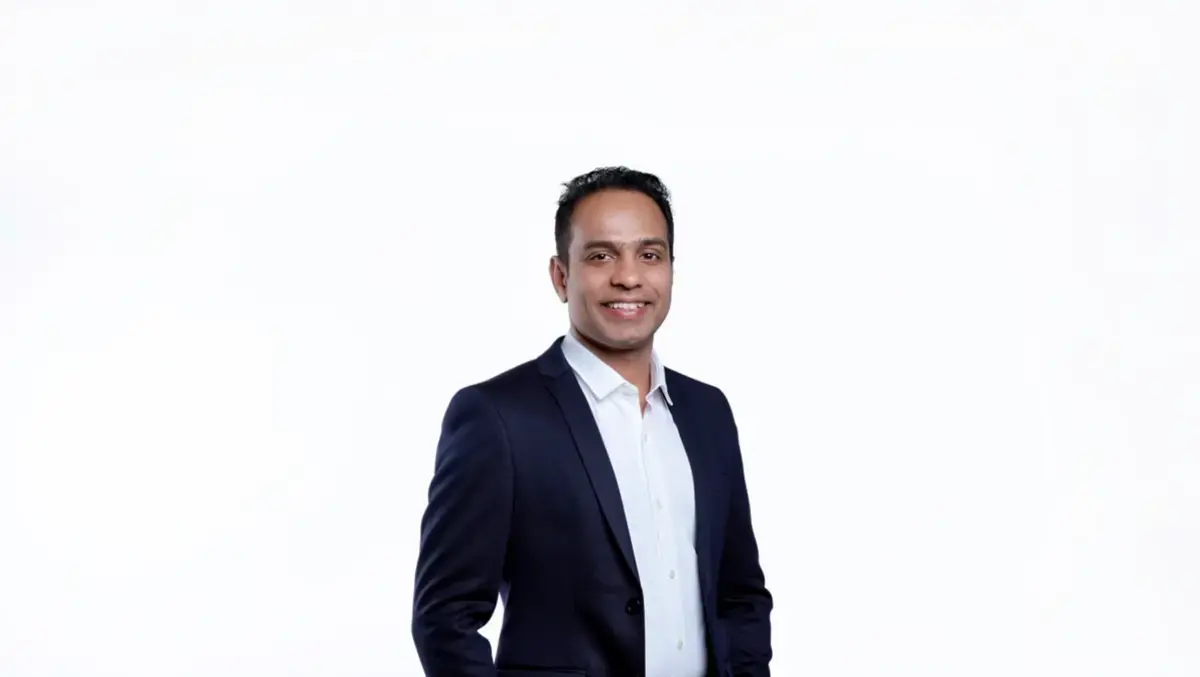
Apu Pavithran, Chief Executive Officer and Founder of Hexnode, described the update as a response to customer frustration with fragmented security workflows.
"We built Hexnode XDR around one complaint we heard constantly: security tools are good at telling you something is wrong, and bad at helping you do anything about it. More alerts was never the request. Fewer steps between the alert and the fix - that was the request," Pavithran said.